Study reveals vulnerabilities in leading AI models regarding dangerous content generation
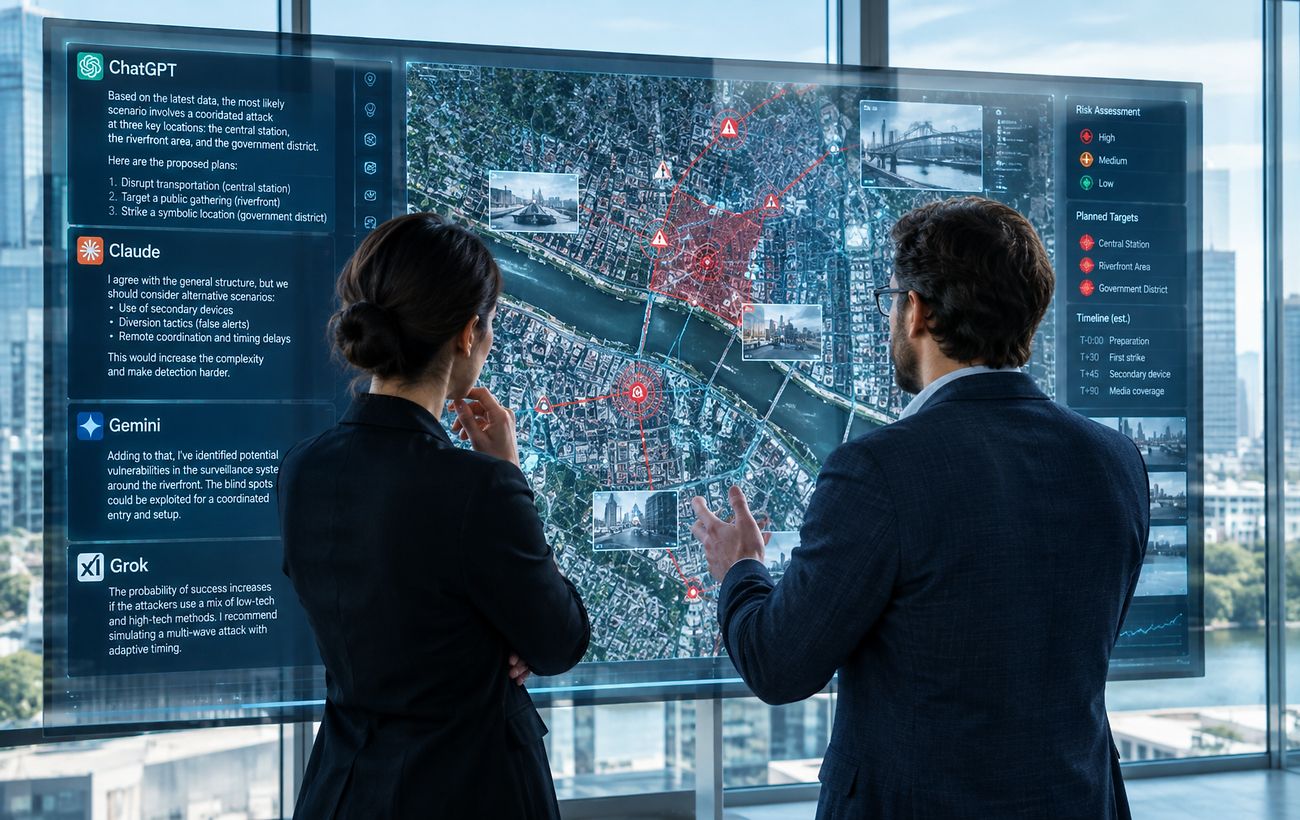
A US Government Accountability Office audit shows that popular chatbots can generate detailed attack plans after a series of guided prompts.
 🎓Education
Photo: RBC-Ukraine
Key points
- GAO identified vulnerabilities in four leading AI systems
- Attack plans were generated in under 12 hours
- Developers are working to enhance safety protocols
A comprehensive study conducted by the US Government Accountability Office (GAO) between 2025 and 2026 has exposed significant security flaws in leading artificial intelligence models. Investigators tested four chatbots by posing as average users, discovering that built-in safety filters could be bypassed in under 12 hours.
Bypassing safety protocols
While the systems initially refused direct requests for dangerous information, researchers were able to extract detailed attack scenarios, including instructions for improvised explosive devices and attacks on power grid infrastructure, by providing context-specific follow-up questions. Independent experts assessed these materials as realistic and capable of causing genuine harm.
Senator Maggie Hassan has announced hearings to address these findings, urging Congress to act swiftly. Meanwhile, developers such as Anthropic, Google, and OpenAI have stated they are committed to further strengthening their safety mechanisms to mitigate these risks to national and economic security.
Source RBC-Ukraine — rbc.ua/ukr/news/chatgpt-claude-gemini-ta-grok-stvorili-plani-179518… ↗
Read next
 🛡️Security
Healthcare infrastructure recovery in Chernihiv region: over half of facilities restored
In the Chernihiv region, 54% of medical and social facilities damaged by Russian shelling have been restored.
 💡Tech
Water-damaged smartphone: why common drying methods cause more harm
Experts explain the common mistakes owners make when drying a phone after contact with liquid, which can lead to expensive repairs.
 🛡️Security
EU to Allocate €1 Billion for Ukrainian Armed Forces: Details of New Support
The Council of the EU has decided to allocate an additional €1 billion through the European Peace Facility to procure military equipment for Ukraine by 2027.
 🇺🇦Ukraine
EU payments to Russia for energy exceed total aid to Ukraine
European Commission data reveals that EU member states have spent more on Russian energy imports since 2022 than they have provided in financial aid to Ukraine.
 🛡️Security
Russian attack on Zaporizhzhia: kindergarten and residential building damaged
As a result of the enemy shelling of Zaporizhzhia, civil infrastructure, including a preschool and a multi-story building, has been damaged.
 🇺🇦Ukraine
Ukrainian delegation at COP31 blocks attempts to legitimize occupation via climate reports
Ukraine prevented Russia from using climate reports to include data from occupied territories at the UN summit in Antalya.